RedTeam (SN61) is taking its cybersecurity technology into banking, with three companies in the top 10% of the Fortune 500 now in its integration pipeline.
RedTeam is the Bittensor subnet operated by Innerworks, a cybersecurity company building tools to detect and defend against online threats. The update came during a recent appearance on Novelty Search (NS), where Innerworks CEO Oscar and lead developer Javokhir discussed the subnet’s latest commercial progress.
RedTeam said it has completed testing with a security-industry partner and is now working toward integrations with the three banking companies. The projects are currently moving through security and compliance processes, with the team expecting a contract to potentially be completed by the end of the year.
For a subnet that has built much of its early commercial traction around crypto and identity-related security, banking would represent a significant expansion of its addressable market.
And the team sees the relationship as mutually reinforcing. Every new enterprise deployment exposes RedTeam to new traffic, attack patterns and security requirements, giving the subnet more problems for its miners and automated systems to solve.
One Enterprise Pilot Has Already Converted
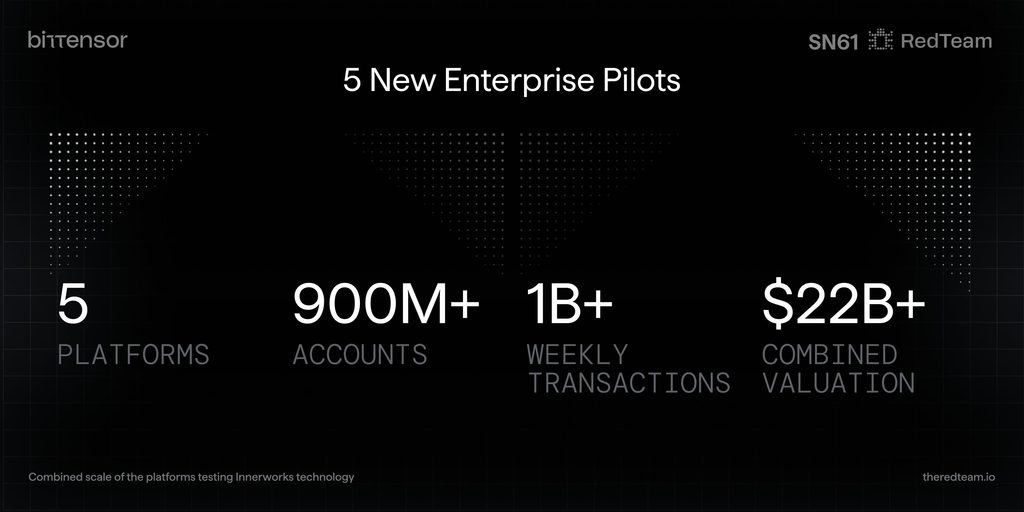
RedTeam also disclosed that one of its five enterprise pilots has converted into a commercial customer since its last public update.
The company said it was benchmarked against multiple security providers during the customer’s testing and procurement process and was the only vendor to make it through.
The customer had never previously adopted an external security tool for the particular use case. However, RedTeam did not name the company for confidential reasons.
That result adds another piece of evidence to the commercial case that The TAO Daily covered in our previous report on the subnet’s Immune System, which explains how RedTeam uses Bittensor’s miner network to continuously generate and test new attack vectors.
The Immune System Is Scaling
The NS appearance also showed how that system has progressed since our previous coverage.
RedTeam demonstrated an automated attack-and-defense loop that can take a miner submission, evolve it into new attacks, and then develop defenses against those attacks.
In one run, a single miner submission was used as the seed for three new attack variants, with the resulting defense changes packaged for deployment.
The important part is that miners remain the source of the initial novelty. RedTeam’s internal agents can then access its own defense code and use that information to push the attack further than an outside contributor could.
The team said it has not needed humans to manually reverse-engineer individual miner submissions for almost a year.
A Bigger Commercial Flywheel
RedTeam also gave clearer insights on how it sees the relationship between Innerworks and SN61.
The company’s commercial growth provides the capital and customer exposure needed to expand the subnet, while the subnet’s decentralized R&D network provides the security advantage that helps Innerworks win those customers.
The team reiterated its commitment to 90% perpetual owner emissions conviction, with more than one million alpha currently committed.
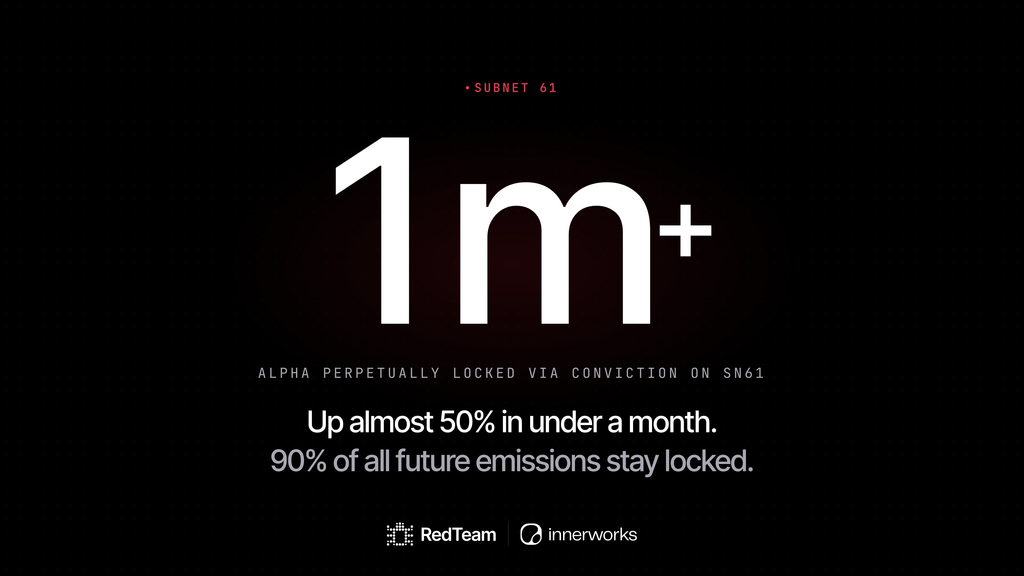
It also said it plans to resume its subnet buybacks after a roughly month-long pause related to its corporate setup and access to TAO.
It’s interesting to note that if even one of the three Fortune 500 companies moves into production, RedTeam would have another major enterprise environment feeding new security problems into the network.
For SN61, the next stage is no longer simply proving that its model works, but proving how far that model can scale.
Watch the full podcast appearance below:
Enjoyed this article? Join our newsletter
Get the latest TAO & Bittensor news straight to your inbox.
We respect your privacy. Unsubscribe anytime.
Enjoyed this article?
Join our newsletter
Get the latest TAO & Bittensor news straight to your inbox — every morning before markets open.
No comments yet — be the first.